Posts

Showing posts with the label firewall

Firewall scripts.

Image
Use any of this information at you own risk. Basics The essence of security is simplicity, and when it comes to workstation or small-office Linux firewalls I have always been a fan of direct iptables use over some of the more popular alternatives ([g]ufw, fwbuilder). While they may be easier to use, they also hide a lot of the details. Especially when you are starting to learn about firewalls and network security, I believe you are better served using customizable firewall scripts like the two I detail below. When you get comfortable with iptables and networking concepts, then you can look to some of the other solutions. At that point, you'll fully understand what they are doing under the hood. Iptables Scripts The first aptly-named shell script, 'firewall.sh', is meant to protect a SOHO (Small Office / Home Office) or home office network behind a dual-homed (two interface) firewall. It doesn't support DMZ hosts, but does support the most common ...

Software as a service. (SAAS)

Image
Talked about IAAS a while back, now here is another part of the cloud. From Wikipedia - History of SAAS: Centralized hosting of business applications dates back to the 1960s. Starting in that decade, IBM and other mainframe providers conducted a service bureau business, often referred to as time-sharing or utility computing . Such services included offering computing power and database storage to banks and other large organizations from their worldwide data centers . The expansion of the Internet during the 1990s brought about a new class of centralized computing , called Application Service Providers (ASP) . ASPs provided businesses with the service of hosting and managing specialized business applications, with the goal of reducing costs through central administration and through the solution provider's specialization in a particular business application. Two of the world's pioneers and largest ASPs were USI, which was headquartered in the Washington, D.C. are...

Your firewall died and all the stores are closed.

Image
Your router/firewall died and all the stores are closed. What do you do? What do you do?  Time to go to the old parts bin and resurrect some parts. One unique idea about this set up is that instead of using an old fashioned hard drive, we well be using a compact flash card as the drive. For three reasons we do this. First is to cut down on the noise. A quiet pc is an ignored pc. Secondly, we want to cut down on the heat in the machine.  Cooler parts should last longer. And the lastly, to reduce the electricity consumption till you can get a replacement unit if you decide to get one. What is a firewall again. It is a set of hardware and software that insulates your home network from the internet. Just as a firewall is used to keep a fire from spreading, the network firewall is expected to keep your local area network secure to a degree. Nothing is perfect. You can get all kinds of units to protect your network. The network modem in most cases will not protect you. You...

Is your network firewall backdoor open?

Image
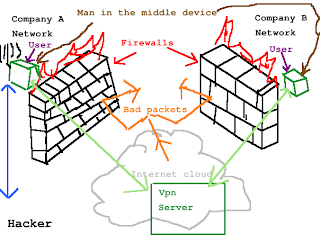
This is going to almost sound like a basis for a script from the old "Mission Impossible" TV show. First a little preparation. If you work for a company or have lots of computers where you live, most likely (at least I hope so) there is a device to control what comes into your network. In general this is called a network firewall. They are set up to keep the bad guys out from the outside. What they do not do is keep a control over what goes from inside to outside the network. If persons or persons want access to your network, trying to get through a firewall is the hardest way in. If they could put a device on the inside of your network, then they have you lock stock and barrel. Somehow they get physical access to your facilities and install what is known as a man in the middle device. Your firewall at this point is now worthless. Traditionally man in the middle devices were created from old wifi routers using modified firmware. Generally you had to be nearby to have access t...